Industrial IoT Security Challenges: Risks, Solutions & Best Practices
Walk into almost any industrial site in the UAE right now and you’ll see some version of the same story playing out. A plant hooks its monitoring or predictive maintenance system up to the internet, gets the dashboard running as fast as possible, and figures security can wait until later. Sometimes that “later” never quite arrives. It’s not really negligence. It’s just a good idea moving faster than the security thinking behind it — and closing that gap is a big part of what we do at C3 Automation when we work with industrial clients. Bridging that gap is critical in addressing modern IoT security challenges.
That’s the environment Industrial IoT security challanges lives in today. Equipment that’s been humming along for twenty or thirty years, none of it designed with networking in mind, is now online and talking to systems it was never built to talk to. The numbers back up why this matters. IBM’s 2024 Cost of a Data Breach report put the average breach cost in the industrial sector at $5.56 million — 13% higher than the global average across all industries. Iot security challanges
Manufacturing and transportation together account for roughly 40% of all IoT security challanges in malware incidents, according to IoT security challanges firm ORDR, and Verizon’s Data Breach Investigations Report found that roughly one in three breaches now involves an IoT device somewhere in the chain. These aren’t edge cases anymore — they’re the baseline risk of running a connected plant.his highlights how critical it is to address IoT risks alongside adopting cloud security services that protect connected environments
What Is Industrial IoT (IIoT), Really?
IoT, stripped down to basics
IoT — the Internet of Things — is the umbrella term. Any physical object with sensors and a connection that lets it collect and share data counts.
Your smartwatch counting steps. A thermostat that’s figured out your schedule. A fridge that reminds you the milk’s gone bad. All of it falls under IoT security challanges
The common thread: something senses a bit of the physical world and turns it into data a system can use. Smart home devices, fitness trackers, connected cars
IIoT: same idea, much higher stakes
IIoT takes that concept and drops it somewhere the consequences are a lot more serious — factories, power grids, oil and gas pipelines, water treatment plants, transportation networks.
Instead of a watch nudging you to stand up, you’ve got sensors watching turbine vibration, actuators cracking open valves on a chemical line, and control systems making split-second calls that affect output, safety, and sometimes people’s lives. Smart factories, predictive maintenance systems, industrial robots and sensors The underlying tech overlaps quite a bit. What happens when it breaks does not.
The building blocks worth actually understanding
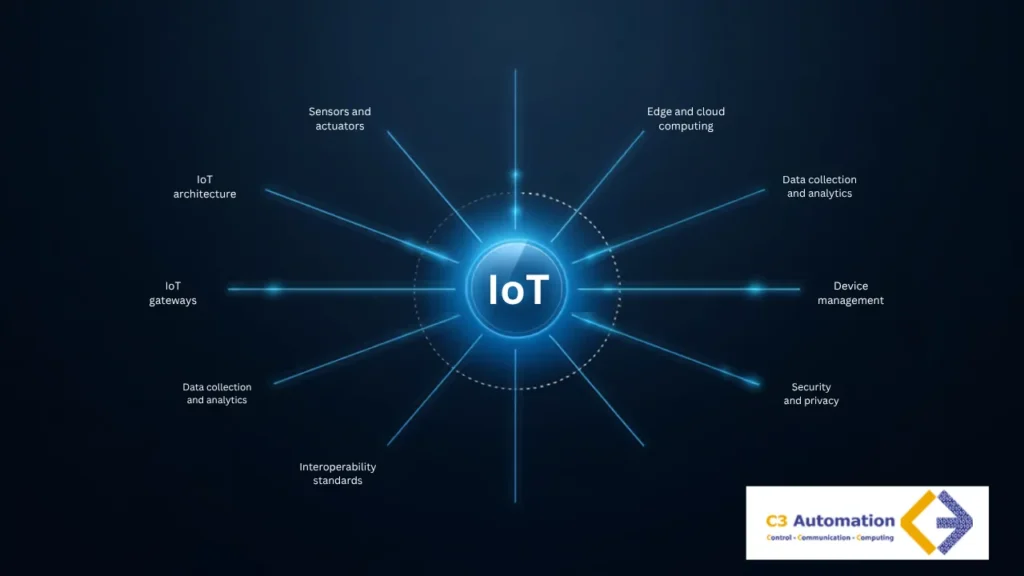
Before getting into the iot security challenges themselves, it’s worth having this vocabulary straight — a lot of the gaps we see trace back to teams not fully grasping one of these pieces.
1. Connected devices (“things”) — physical hardware with sensors, software, and connectivity baked in, anywhere from a factory-floor vibration sensor to a home smart speaker
2. Sensors and actuators — sensors read the physical world (temperature, pressure, motion); actuators do the opposite, turning a digital signal into a physical action like opening a valve
3. Connectivity — Wi-Fi, Bluetooth, Zigbee, LoRaWAN, cellular — each chosen for range, power draw, and speed. No connection, no data
4. IoT architecture — four layers working together: perception (gathering data), network (moving it), processing (making sense of it), application (putting insight in front of a person)
5. Edge and cloud computing — edge handles data close to the device for instant responses; cloud takes on the heavier analytics further out. Most serious deployments lean on both
6. IoT gateways — the translator between devices and the internet, aggregating data, converting protocols, enforcing local security policy
7. Data collection and analytics — raw sensor data is basically useless until it’s run through descriptive, predictive, or prescriptive analysis. This is what actually powers predictive maintenance
8. Device management — provisioning, monitoring, patching, and eventually decommissioning thousands of devices. Skip this and blind spots show up faster than most teams expect
9. Security and privacy — every connected device is a potential way in, which is exactly why encryption, authentication, and secure boot aren’t nice-to-haves in an Industrial IoT security challanges in a plan
10. Interoperability and standards — protocols like MQTT and frameworks like IEC 62443 let equipment from different vendors work together without opening new gaps
Why Industrial IoT Security Actually Matters
A consumer IoT breach is annoying, maybe a little embarrassing. Someone’s smart doorbell gets compromised — bad week, move on.
A breach in an industrial environment is a completely different category of problem. It can stop a production line, wreck physical equipment, or put a worker in harm’s way. That’s the whole reason Industrial IoT security challanges exists as its own field rather than a subsection of regular IT security.
The business risk isn’t theoretical
An unpatched HVAC controller or an exposed remote access point isn’t just a line item on some audit checklist somewhere. It’s a direct path to downtime — and downtime on a manufacturing line has a dollar figure attached almost immediately, sometimes within hours of it starting.
Beyond the direct cost, there’s regulatory exposure, insurance headaches, and — if the incident goes public — reputational damage that tends to outlast the actual outage.
Data protection isn’t an afterthought here
Industrial systems generate more sensitive data than most people realize — production volumes, proprietary process configurations, supplier and customer information moving through connected supply-chain systems.
A breach here isn’t just an IT cleanup job. It can hand a competitor your entire operational playbook, and there’s no patching that after the fact.
This isn’t hypothetical. In 2020, attackers breached the control systems of an Israeli water treatment facility and attempted to push chlorine levels to dangerous concentrations — an operator caught it before it caused harm, but the incident became a widely cited case study in exactly why industrial iot security challanges gets treated as a physical-safety issue, not just a data one. Security researchers have since warned that similar attacks on industrial control systems carry the potential for real casualties, not just downtime.
IoT Security Challenges: The Hidden Risks
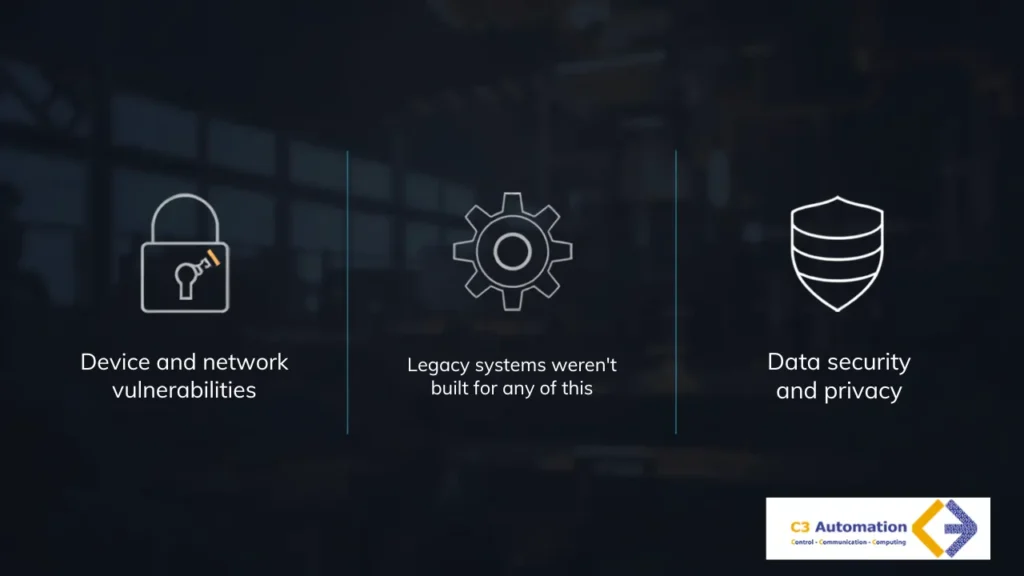
Device and network vulnerabilities
Most IIoT deployments run dozens of device types from different manufacturers, each with its own firmware, its own patch cycle (or lack of one), and its own default settings. That inconsistency is exactly what attackers go looking for — the weakest device on the network sets the ceiling for how secure the whole thing actually is.
Weak authentication and access control comes up constantly. A surprising number of industrial devices still ship with default credentials nobody bothered to change, or access rules built for a world where “physically on-site” was assumed to mean “authorized.” Neither assumption holds up anymore.
Scale makes this harder, not easier. Securing ten devices is an afternoon’s checklist. Securing ten thousand devices across multiple sites, each running different firmware, is an ongoing grind — and it’s usually where these programs quietly start falling behind.
Legacy systems weren’t built for any of this
A lot of the equipment running today’s factories predates the very idea of network security. That’s not really a knock on the equipment — it just wasn’t the threat model anyone had in mind when it went in twenty years ago.
Outdated equipment is a standing liability. Machinery that can’t run modern authentication or encryption becomes the weak link the moment it’s connected to a broader network, no matter how tight everything around it is. This is one of the tougher problems to solve, since ripping out perfectly functional equipment purely for security reasons is a hard sell to a finance team.
Data security and privacy
IIoT systems are constantly generating operational data — some sensitive, some commercially valuable, most of it flowing across systems that were never designed with data protection as a first principle. Where that data goes once it leaves the factory floor is really a cloud problem, which is worth breaking out on its own below.
Cloud Security Services: The Safety Net
Cloud platforms have become central to Industrial IoT security challanges not despite the scale of industrial data but because of it. Real-time monitoring, centralized policy enforcement, elastic processing power — genuinely hard to replicate with on-premises infrastructure alone, especially once you’re running more than one site.
Cloud security services bring purpose-built tools to the table: threat detection tuned to industrial traffic patterns, automated compliance checks, centralized visibility across sites that would otherwise report into separate, disconnected systems. Done well, cloud security services turn a dozen scattered dashboards into one picture someone can actually act on.
Cloud Security Architecture: The Foundation
Cloud security architecture matters more as adoption grows. As more industrial data and processing shifts to the cloud security architecture behind it needs to be deliberate: access controls, encryption in transit and at rest, and a clear owner for each layer. Get the cloud security architecture wrong early, and every workload built on top of it quietly inherits the same weakness.
Done properly, cloud security architecture is the structured set of policies and controls governing everything sitting in the cloud — applications, storage, and the connected IIoT devices feeding data into it. Get this framework right early, and everything built on top of it is far easier to defend later. Get it wrong, and you’re retrofitting security onto systems that are already live, which is always the harder way to do it.
Multi Cloud Security: The Gaps That Matter
Multi cloud security adds real complexity. Running workloads across more than one cloud provider is common now, mostly for resilience and flexibility, but each provider brings its own tools, policies, and configuration quirks. Multi cloud security means holding consistent protection across several different rulebooks at once — and the gaps that actually matter tend to show up right at the seams between platforms, not inside any one of them.
Solutions to Industrial IoT Security Challenges
There’s no single fix here, and anyone selling one is oversimplifying. Industrial IoT security challanges has to be layered, because the risk itself spans devices, networks, data, and cloud infrastructure all at once. Strong authentication and encryption close off the most common entry points first. Multi-factor authentication, unique credentials per device, encryption for data in transit and at rest — this should be the baseline every program starts from, not the upgrade you get around to eventually.
Network segmentation limits the blast radius when something does go wrong, and eventually something will. Splitting a flat network into smaller, purpose-specific zones means a compromised sensor on the factory floor can’t automatically reach the systems managing safety controls or business data.
Best Practices That Actually Hold Up
Zero Trust security : Flips the old assumption on its head. Instead of trusting anything already inside the network perimeter, every device and user has to verify continuously, every single time. For IIoT environments running hundreds of unattended devices, this matters more than it does almost anywhere else in enterprise security.
Regular monitoring and updates : Sound almost too obvious to bring up, but they’re consistently where these programs slip in practice. A device that isn’t monitored can stay compromised for months before anyone notices. A device that isn’t patched stays exposed to threats that were already fixed everywhere else a long time ago.
Conclusion
Industrial IoT security challanges is reshaping how factories, utilities, and supply chains run — faster decisions, less downtime, tighter visibility into operations. None of that’s really up for debate anymore. What is worth repeating: Industrial IoT security challanges has to be built for this environment specifically. It can’t just be borrowed from a standard IT playbook and hoped to fit. Getting it right means treating devices, networks, data, and cloud infrastructure as one connected risk surface — not four separate checklists handled by four separate teams. Strong authentication, deliberate network segmentation, solid cloud security architecture, and dependable cloud security services cover the technical layer.
Zero Trust security, multi cloud discipline, and consistent monitoring are what keep it that way month after month, not just at launch. These challenges aren’t going away as adoption grows — if anything, they’re stacking up. But the organizations that treat Industrial IoT security challanges as an ongoing operational habit, not a one-time project, are the ones that don’t end up as the case study everyone else learns from.
We’ve watched this play out across enough industrial sites in the region to say it plainly: the plants that hold up best under pressure aren’t the ones with the biggest security budgets. They’re the ones where patching, access reviews, and network segmentation just became part of how the place runs — not a project that got a kickoff meeting and then quietly stalled. That’s the difference that actually shows up when something goes wrong. By investing in cloud security services, building a resilient cloud security architecture, and implementing effective multi cloud security, organizations can protect their operations and ensure long-term success.
FAQ
What are the biggest IoT security challenges facing Industrial IoT (IIoT) today?
Device vulnerabilities, weak authentication, aging legacy infrastructure, unsecured networks, and inconsistent monitoring top the list — largely because IIoT environments combine so many device types and vendors under one roof, each with its own security posture.
Why does IIoT security get treated differently from standard IoT security?
Because the consequences are physical, not just digital. IIoT sits inside power plants, factories, and transport networks, so a breach can mean operational downtime, financial loss, or a genuine safety incident — not just a data leak someone apologizes for later.
What can businesses actually do to improve Industrial IoT security?
Start with strong authentication and encryption, add network segmentation to limit exposure, keep systems patched on a real schedule rather than an aspirational one, and move toward a Zero Trust model instead of assuming anything inside the network is automatically trustworthy.
What role do cloud security services play in Industrial IoT security?
They centralize monitoring and policy enforcement, scale with the volume of data IIoT generates, and bring in threat detection tools that would be genuinely difficult to build and maintain on-premises alone.
What makes multi cloud security so complicated for IIoT?
Every provider comes with its own tools, policies, and configuration defaults. Multi cloud security means holding consistent protection across all of them — and the risk usually shows up in the gaps between platforms rather than inside any one of them.